In short
A confidential file pasted into a consumer chatbot can be used to train the model, and stay there for years. The free versions of ChatGPT and Claude learn from your exchanges by default. Enterprise plans and APIs do not: they contractually commit to not training on your data, with zero retention available. So the risk is not AI itself. It is consumer AI used without guardrails. A serious studio handles your assets under NDA, in a no-train environment, and keeps AI upstream, never on the final deliverable.
On a Sunday evening, an art director pastes your next fragrance's packaging into a chatbot to “see what it would look like” in 3D. The product has not launched. The brief is under embargo. The file has just left your company, and nobody decided that.
The gesture has become ordinary. That is exactly what makes it dangerous. The right question is not “should we ban AI,” nobody will win that fight. It is “where do our files go, and who gets to read them.” Here is the answer, without drama and without wishful thinking.
The real risk is not AI. It is consumer AI.
Nearly six employees in ten already use AI at work, most often on their own initiative, and barely one in three says their company has a clear policy on the subject (KPMG and the University of Melbourne, 2025, 48,000 respondents in 47 countries). The gap between those two numbers is exactly where your assets travel without a net.
It is called shadow AI: AI used outside any approved framework, often from a personal account. In 2025, one organization in five reported a data breach tied to shadow AI, according to IBM's breach cost report. And those incidents cost more than average: roughly 670,000 dollars more per breach in organizations where shadow AI is widespread, with a markedly higher rate of intellectual property theft. The 2026 edition of the same report drives the point home: one malicious breach in four now involves AI. This is not a theoretical worry for a CISO. It is a line on a balance sheet.
- ◆1 in 5 : organizations that suffered a data breach tied to shadow AI in 2025 (IBM)
- ◆+$670,000 : average extra cost per breach where shadow AI is widespread (IBM, 2025)
- ◆58% / 34% : employees who use AI at work, vs employees whose company has a clear policy (KPMG, 2025)
Here is the point that matters: the danger does not come from the technology. It comes from the door you walk through. The same tool, ChatGPT or Claude, behaves in two radically different ways depending on the version you access it through. And almost nobody notices the difference.
What happens to a file pasted into a chatbot
When you drop an image or a document into the consumer version of a chatbot, two things happen. The file is stored. And, unless you change a setting, it can feed the training of the next model.
This is not a rumor, it is written in the terms. Since fall 2025, Claude uses consumer conversations to train its models unless you explicitly opt out, and the setting offered on screen is switched on by default. If you accept, retention climbs to as much as five years. On the OpenAI side, consumer ChatGPT exchanges also feed model improvement by default. The logic is the same everywhere: the free product is paid for with your data.
Professional plans flip the rule. APIs, Anthropic's Team, Enterprise and Edu plans, OpenAI's API and its Business and Enterprise offerings: all commit to not training on your inputs or outputs, with SOC 2 certification and, often, a zero retention option. Same brand, same model, opposite guarantees. Everything hinges on the contract you did not read.
In practice, a confidential packaging pasted into a free app can be stored, analyzed, and in theory contribute to a model your competitors will query tomorrow. The odds of it resurfacing verbatim are low. The problem is not the odds. It is that you have lost control, and a confidentiality agreement signed with you no longer protects anything.
The five questions to ask your studio or agency
You do not need to be a cybersecurity expert to assess a partner. Five questions are enough to tell those who have thought about it from those who improvise.
1. Which version of AI do you use on our files?
The right answer mentions enterprise plans or APIs with a no-training commitment. If the reply is just “ChatGPT” with no detail, that is the consumer app, and your assets can be used to train the model.
2. Do you enable zero retention for our data?
Professional plans often let you keep no trace of files after processing. A studio that knows this setting has probably switched it on. A studio discovering the term in front of you never has.
3. Does your NDA name AI tools?
A confidentiality agreement written before 2023 says nothing about AI. Yours must name these tools explicitly and forbid feeding them your confidential assets outside approved environments. Otherwise it protects a world that no longer exists.
4. When does AI step in?
Upstream, on exploratory directions that do not yet contain your secret? Or straight on the deliverable, with your real files? The two answers do not carry the same level of risk, nor the same final quality.
5. Do our files leave your pipeline?
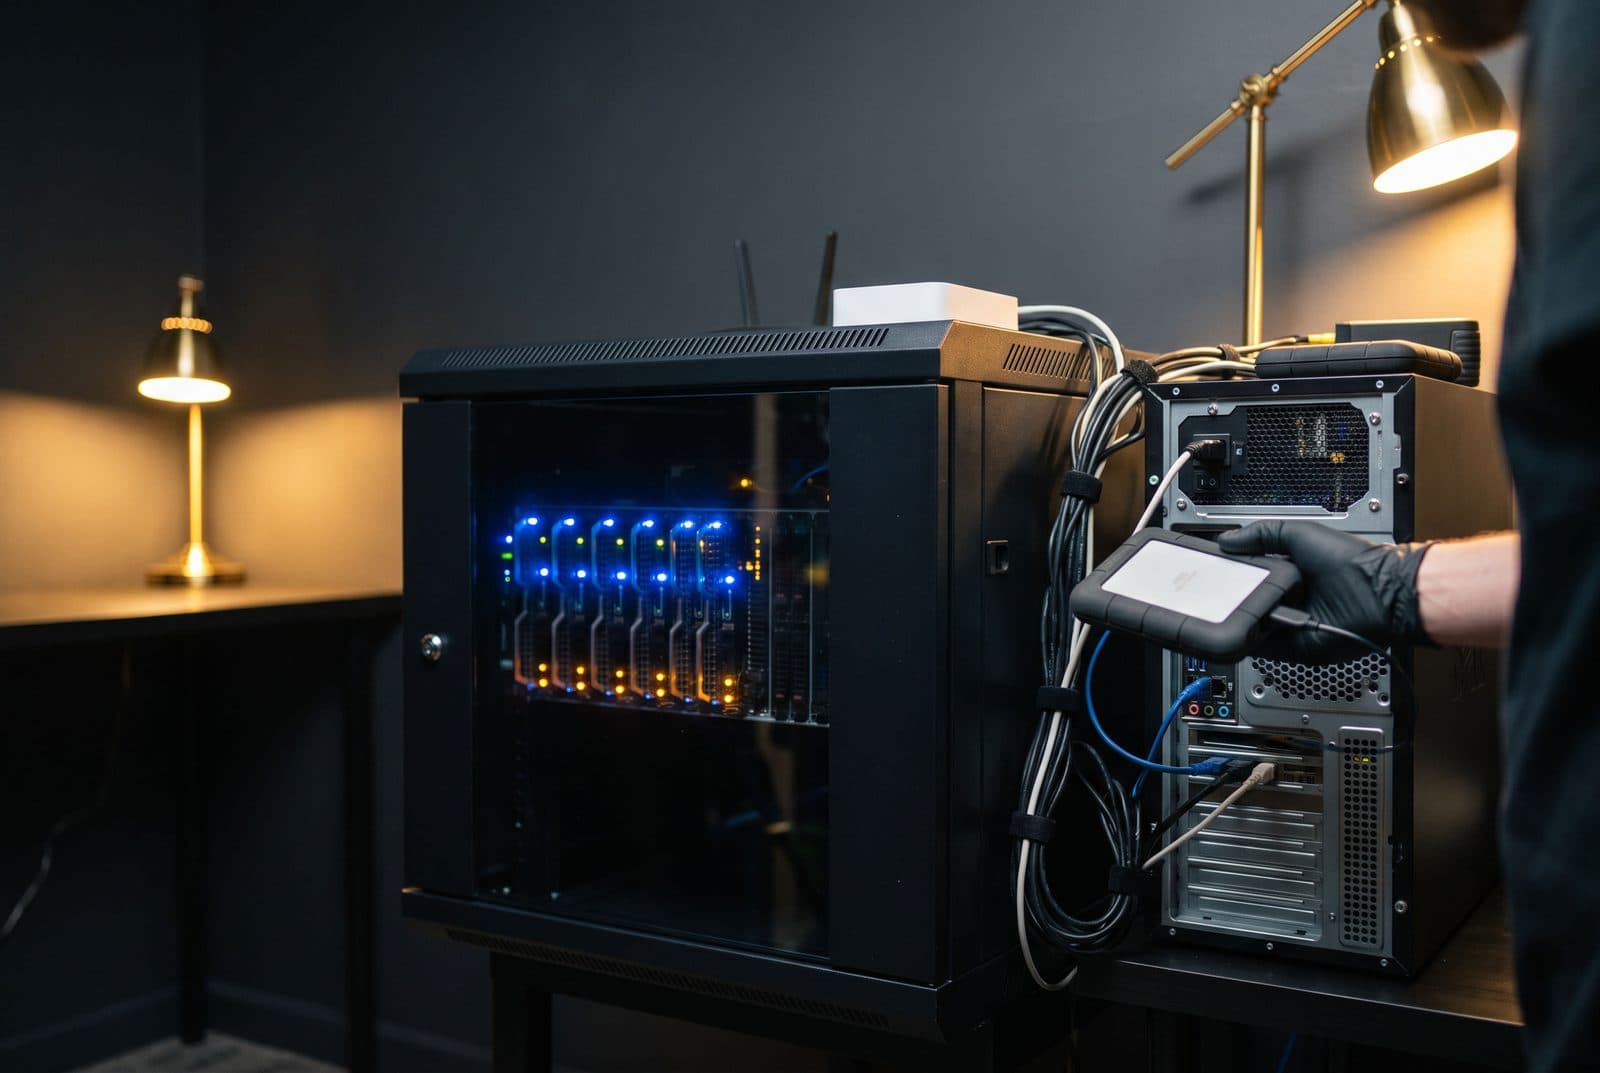
A studio controls its chain when your assets stay on its machines and its controlled environments, from the first file to the master. The moment a file goes off to a consumer tool, the chain is broken, and your NDA with it.
A studio that cannot tell you which version of AI your files pass through should not be receiving them.
The legal trap: a 100% AI image is not yours
There is a second risk, less known, and it touches ownership. An image generated entirely by AI, from a simple prompt, is not protectable by copyright. This is not an opinion: in January 2025 the U.S. Copyright Office confirmed it, and in March 2025 the federal appeals court in Washington ruled the same way, a decision that became final when the Supreme Court declined to hear the case in March 2026. Without substantial human contribution, no author, therefore no exclusive right.
Translated for a brand, that means a key visual produced “all AI” falls into a dangerous grey zone. You cannot really claim it as yours. Competitors could come close to it with no recourse for you. Add that most platforms restrict commercial use of their outputs in their terms, and that those outputs can resemble protected works seen during training. A single visual can therefore be both impossible to own and risky to use.
That is one of the reasons that, with us, the final deliverable is never a raw generator image. It is built in 3D and compositing, by artists, from assets you fully own. This is not a pose. It is what lets you register, adapt and defend your campaign.
How Digiteyes handles your assets
Our rule fits in one sentence: AI lives upstream, never on the final deliverable, and never on your confidential files inside an open tool.
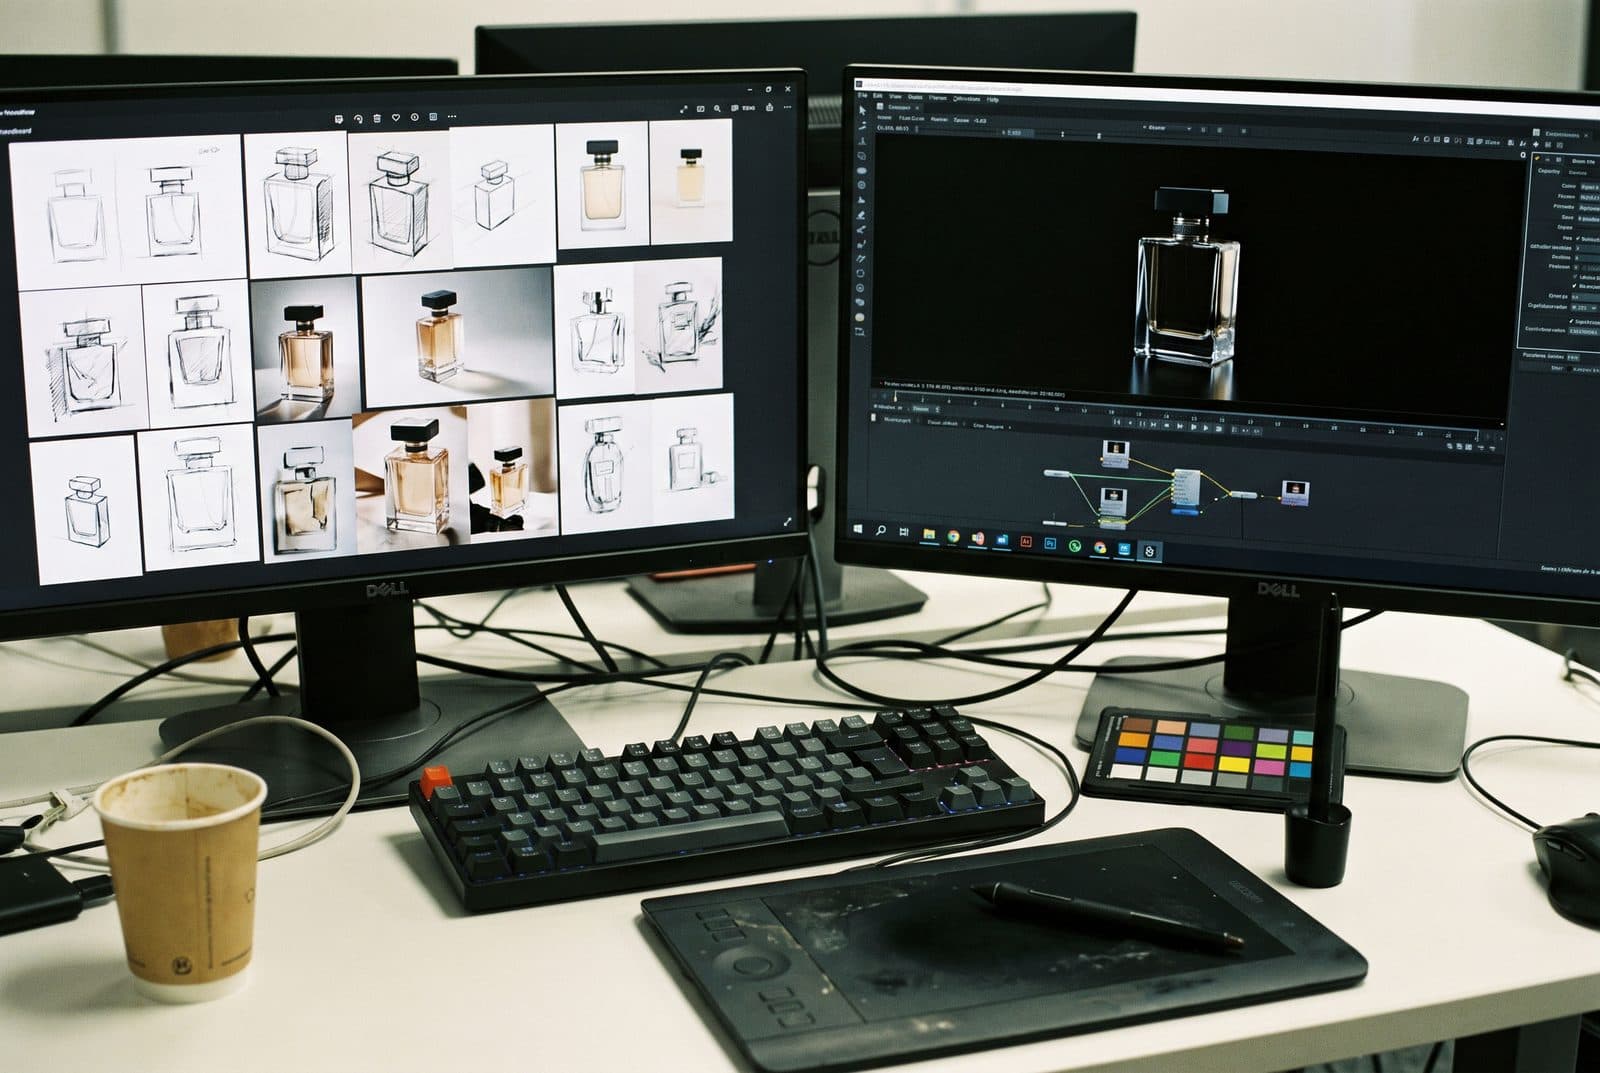
In pre-production, we use AI to explore: moodboards, lighting moods, previews, brand worlds. That phase works on directions and references, not on your packaging under embargo. When a project requires handling sensitive data, it happens in professional environments that do not train on our data, with retention cut to the strict minimum. Your files stay on our pipeline, from brief to master.
The deliverable itself is modeled, animated and composited by hand. You get a 3D asset you own, clean legally, reusable for years.
What about the European framework?
For a European brand, two texts stack up. First the GDPR: as soon as an asset contains personal data, you are the controller, the tool is only a processor, and you need a written agreement plus real data minimization. Then the AI Act, applicable in stages since 2025, whose transparency obligations on generated content (Article 50) have applied since August 2, 2026. A serious partner already works within this frame. Asking them is a good maturity test.
Frequently asked questions
- ◆Is it dangerous to use AI on a confidential brand project? The danger does not come from AI itself, but from the version used. A file dropped into a free consumer app can be stored and used to train the model. The same task run in an enterprise plan or an API, with a no-training commitment and zero retention, does not carry that risk. It all depends on the framework.
- ◆Are my files used to train AI? In the consumer versions of ChatGPT and Claude, by default yes, unless you change a setting. Since fall 2025, Claude trains on consumer conversations unless you explicitly opt out, with retention that can reach five years. APIs and enterprise plans commit, for their part, to not training on your data.
- ◆How do I know if a provider protects my assets? Ask them five questions: which version of AI they use, whether they enable zero retention, whether their NDA names AI tools, when AI steps in, and whether your files leave their pipeline. Precise answers point to a studio that has framed the issue. Vague answers are an answer in themselves.
- ◆Can an AI generated image belong to me? An image produced entirely by AI from a prompt is not protectable by copyright, as the U.S. Copyright Office and the federal courts confirmed in 2025, followed by the Supreme Court's refusal to reopen the question in 2026. Only a substantial human contribution opens protection, and only over the human part. For a brand visual meant to be registered and defended, a deliverable built in 3D by artists is safer.
- ◆Does Digiteyes AI touch the final deliverable? No. AI steps in during pre-production, to explore intentions and moods, on non-confidential directions. The final deliverable is modeled, animated and composited by hand, from assets you own. Your sensitive files stay on our pipeline and in environments that do not train on your data.
Unsure about the confidentiality of your project?
Digiteyes builds premium CGI and VFX for demanding brands and agencies, under NDA, from idea to master. Tell us your context and your confidentiality constraints, and we will explain precisely how your assets are handled: contact@digiteyes.fr.
Sources
- ◆IBM · Cost of a Data Breach Report 2025 (2025 and 2026 editions: shadow AI, +$670,000 extra cost, share of breaches)
- ◆IBM Newsroom · 97% of affected organizations lacked AI access controls (governance and access)
- ◆KPMG and the University of Melbourne · Trust, attitudes and use of AI (2025) (AI use by employees, share of employees whose company has a policy)
- ◆Protecto · OpenAI, Claude, Perplexity: privacy compared (consumer vs enterprise training, retention)
- ◆U.S. Copyright Office · Copyright and Artificial Intelligence (non-protectability of 100% AI outputs, January 2025)
- ◆Congressional Research Service · Generative AI and Copyright Law (appeals decision, March 2025)
- ◆Trilateral Research · Image generation, GDPR and the AI Act (European framework, data controller)